Custom AI agent · IT & Security
AI Access Request Processing Agent
Move access requests forward without losing control.
Turn access requests into clear, reviewable decisions with the right approvals, evidence, and least-privilege handoffs.
- More complete requests with the business need, resource scope, duration, and requester context reviewers need
- Fewer delays from misrouted approvals, missing owners, or incomplete entitlement details
- A traceable decision path that keeps authorization, expiration, and exceptions visible
Starting at $300 USD/month
Starting price is $300 USD/month for a tailored solution. Your final proposal defines the request types, approval policies, integrations, usage, deliverables, hosting, support, and payment terms. Additional systems, high-risk workflows, or approval complexity are scoped before work begins.
What is an AI access request processing agent?
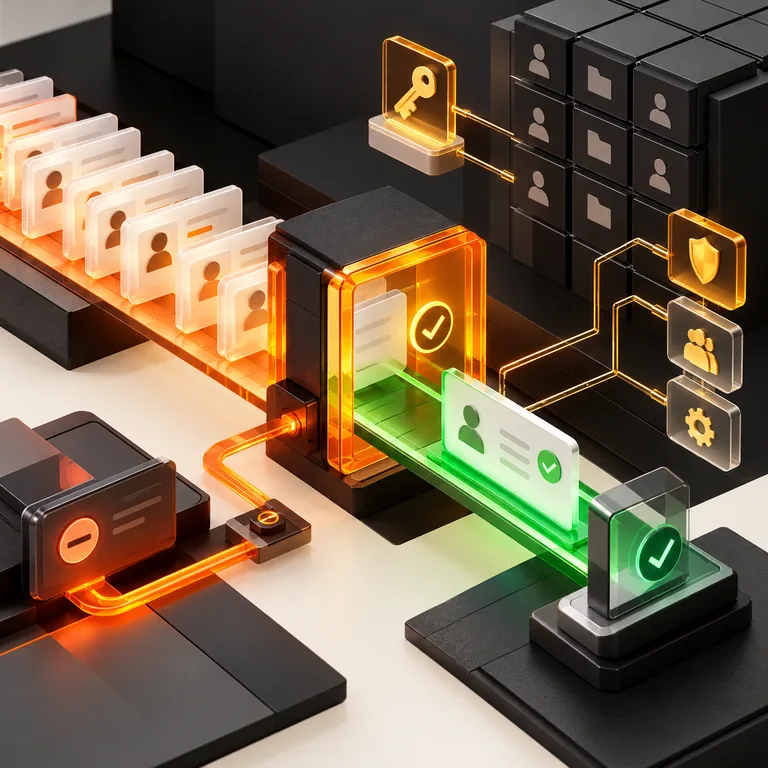
An AI access request processing agent helps security, IT, and business teams handle requests for applications, groups, data, environments, and other resources through a consistent, reviewable workflow. It can collect the requester's purpose, scope, duration, manager or owner context, route the request to the correct approvers, check for missing information, and prepare a decision record. Tranki configures the workflow around your entitlement catalog, least-privilege policy, separation of duties, identity systems, risk signals, expiration rules, and exception process. The agent coordinates and documents the process; it does not grant access, approve its own request, bypass a control, or infer authorization from a vague business need.
What it can process
Collect complete request context
Guide requesters through resource, role, business purpose, duration, environment, data sensitivity, and sponsor details without asking for passwords or secrets.
Route policy-aware approvals
Match the request to resource owners, managers, data stewards, security reviewers, and separation-of-duties rules configured for each entitlement.
Surface risk and missing evidence
Highlight unusual scope, excessive duration, missing ownership, conflicting identity context, or incomplete justification for human review.
Track decision history
Preserve the request, approvals, denials, expirations, exceptions, and source references so teams can explain how an access decision was reached.
Where it can help
Application and group access
Process routine requests for approved applications, collaboration groups, repositories, dashboards, and internal services with the relevant owner checks.
Privileged or sensitive access
Collect the additional justification, duration, approvers, and review evidence required before high-risk access is considered.
Temporary project access
Coordinate time-bound access for projects, vendors, launches, or incident response while keeping expiration and revalidation visible.
How it works
A step-by-step workflow your team can review before launch.
1. Define the entitlement policy
Tranki maps resources, roles, owners, risk tiers, approval chains, separation-of-duties rules, duration limits, and exception requirements.
2. Capture the request
The agent gathers the requester identity, business purpose, scope, duration, sponsor, target environment, and supporting evidence through an approved channel.
3. Validate and route
It checks for missing or conflicting details, identifies the required reviewers, and sends a structured packet without making an authorization decision.
4. Record and follow through
Authorized approvers decide in the designated system; the agent records the outcome, coordinates fulfillment or denial, and monitors expiration or revalidation.
Built around your business
What we configure
- entitlement catalog, roles, resources, owners, data classifications, risk tiers, manager and sponsor rules, approval chains, separation of duties, duration limits, and expiration policy
- connections to approved identity, access-management, HR, ticketing, application, data-governance, collaboration, and audit systems using least-privilege access
- request forms, approval templates, languages, notification cadence, redaction rules, evidence requirements, exception routing, revalidation reminders, and reporting views
What we need from you
- an owned entitlement catalog, resource and data classifications, approval and separation-of-duties policy, identity sources, duration rules, and sample request decisions
- approved authenticated connections to identity, access, HR, ticketing, application, and governance systems with privacy and retention controls
- test cases covering routine access, privileged access, temporary access, contractor requests, conflicting identities, missing owners, denied requests, and policy exceptions
Clear boundaries before launch
What it will not do
The agent does not grant, revoke, elevate, or modify access by itself; approve its own request; bypass separation of duties; decide that a business purpose is sufficient; or expose credentials, tokens, or sensitive data unnecessarily. It should not treat manager approval as a substitute for resource-owner or security review, infer identity from an unverified message, or keep access active past an approved duration. Privileged access, emergency access, regulated data, third-party access, and policy exceptions require the appropriate human and specialist review.
How success is measured
Track request completeness, time to policy-correct routing, approval turnaround, missing-owner rate, denial and rework rate, least-privilege corrections, temporary-access expiration compliance, exception-review completeness, unauthorized-change prevention, and requester satisfaction. Sample approved and denied requests against the entitlement catalog and approval policy to review identity, evidence, separation-of-duties, and retention handling.
Frequently asked questions
What does an AI access request processing agent do?
It collects request details, checks for missing evidence, routes the request to the configured approvers, and maintains a reviewable decision history.
Can it approve or grant access automatically?
Not by default. Authorized owners and security reviewers remain responsible for the decision and fulfillment; automation is limited to workflows you explicitly approve.
Can it handle temporary access?
Yes. It can capture duration, route the required approvals, and coordinate expiration or revalidation when the connected systems support those events.
How does it handle privileged access?
It can apply a separate risk tier, collect stronger justification, and route the request through the additional approval, monitoring, or time-bound controls you define.
What if a request has no clear resource owner?
The agent flags the missing ownership and routes the case for governance or security review instead of inventing an approver.
Does manager approval alone authorize access?
No. The workflow should apply your resource-owner, data-steward, security, and separation-of-duties rules as appropriate to the entitlement.
What is included in the $300/month starting price?
The starting price covers a scoped, tailored solution. The final proposal defines request types, integrations, usage, deliverables, support, hosting, and payment terms.